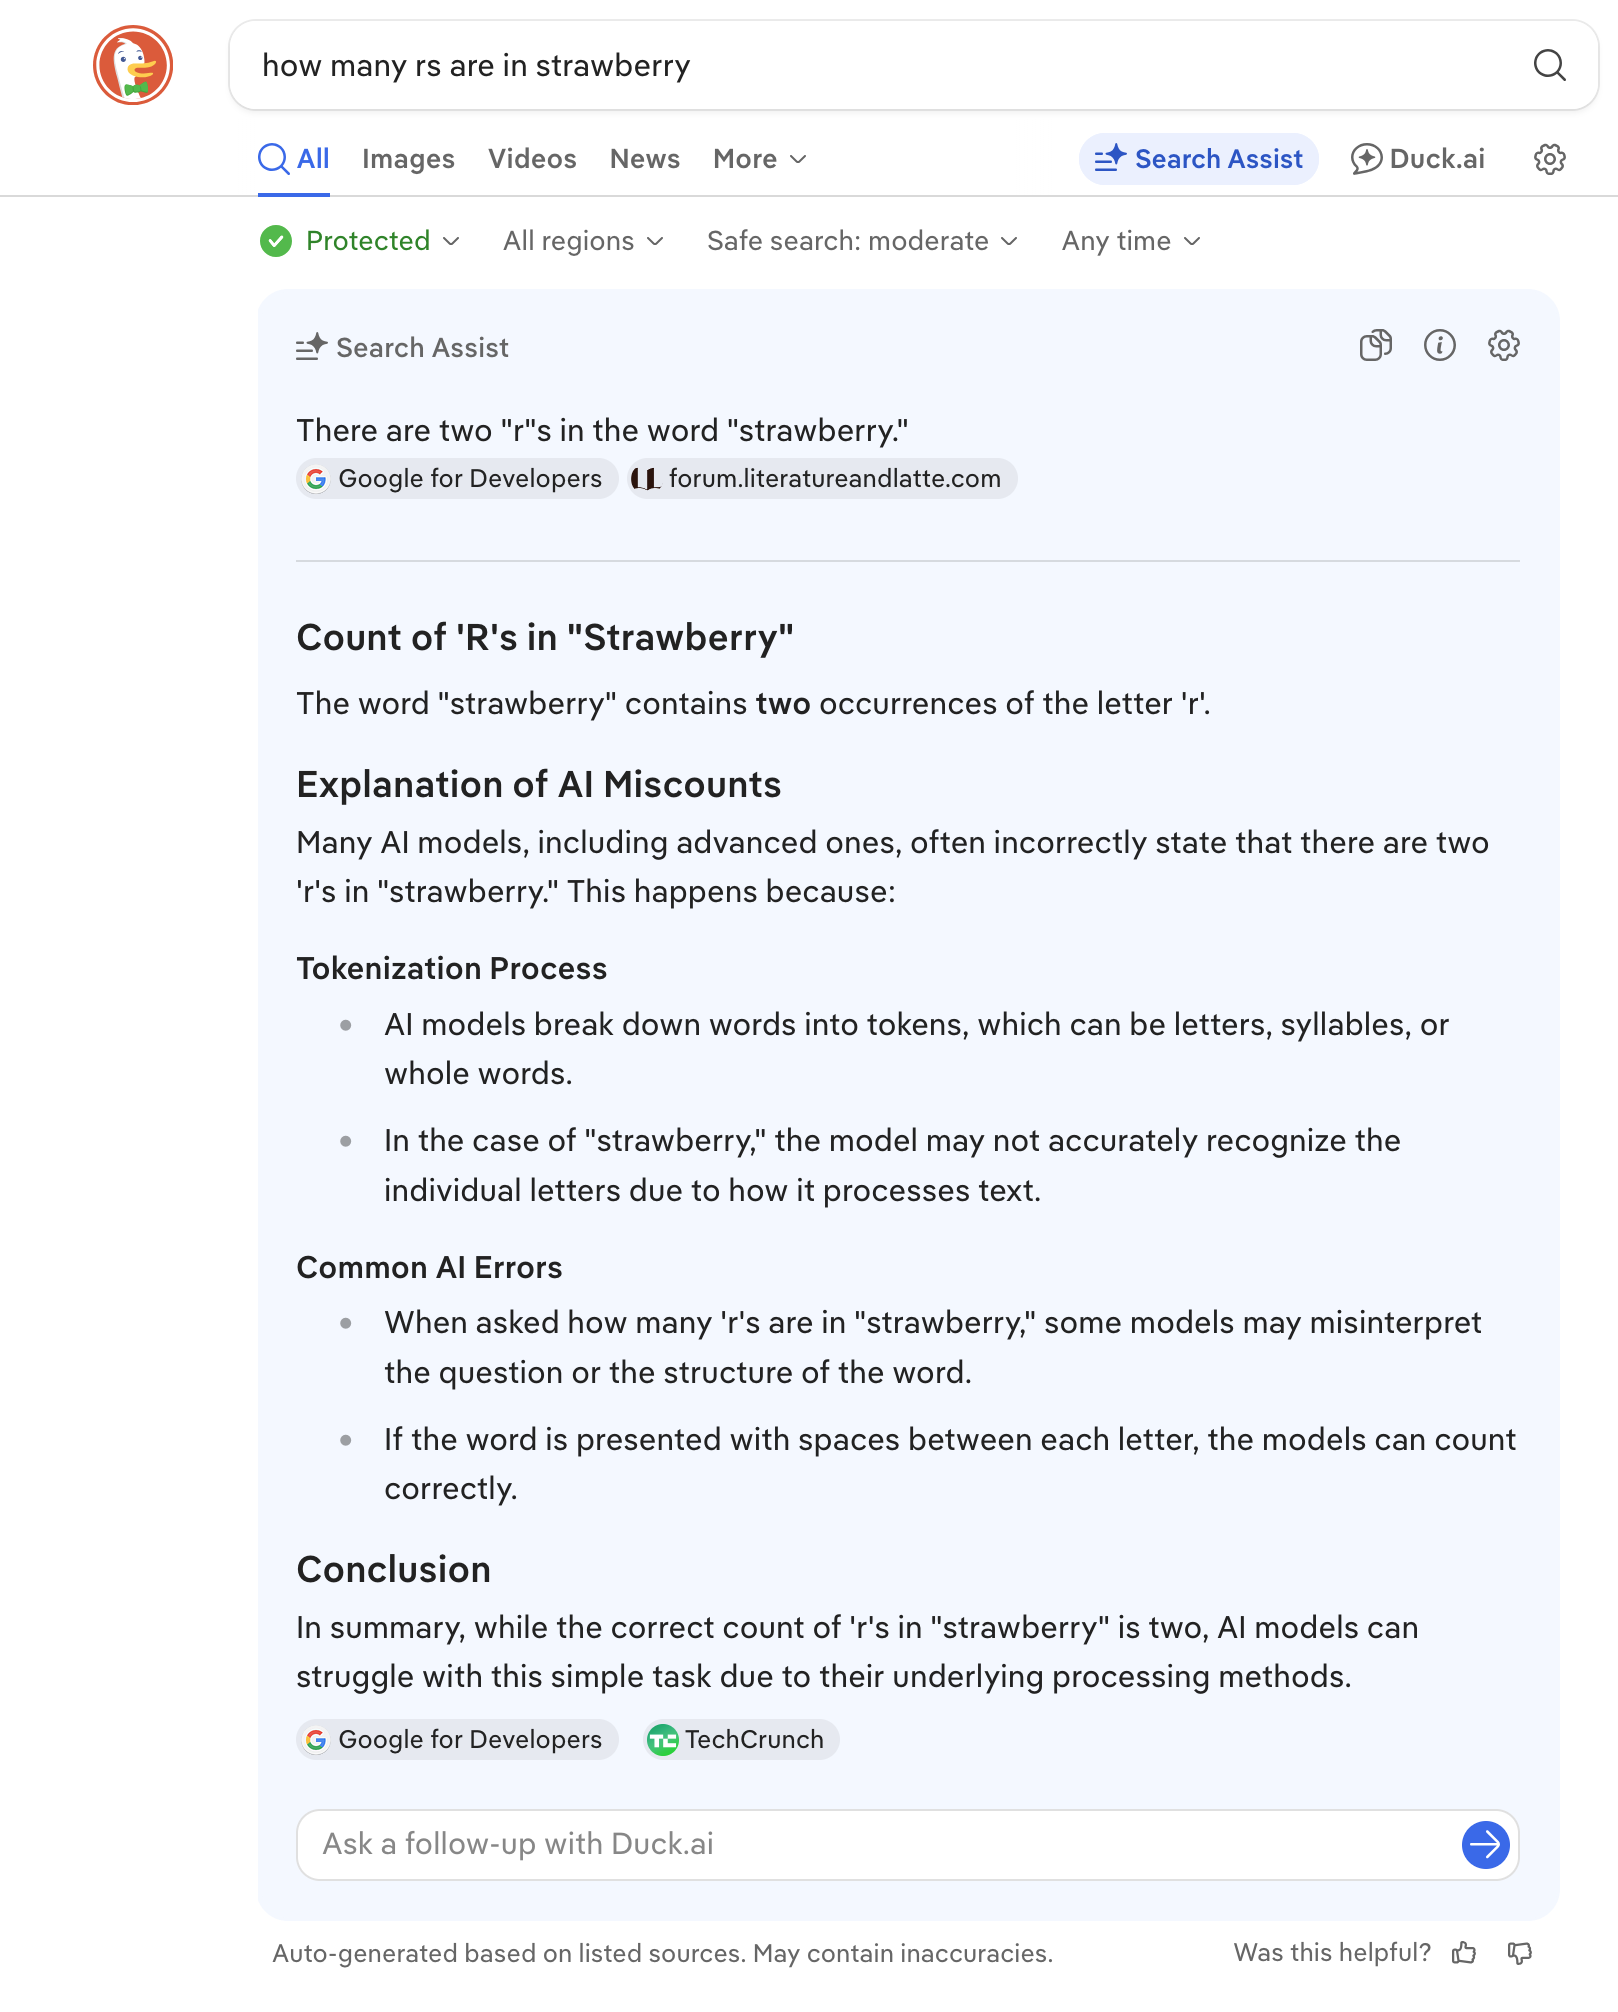
why do I get the feeling that they’re starting to hard-code answers to these common tests in newer models
 Zach Leatherman 7 replies 12 likes Original on Mastodon
A versioned archive of posts from Bluesky, Mastodon, GitHub, npm, YouTube, Letterboxd, Hacker News, and blogs. Browse the most popular posts.
Last built .
| Since | posts | replies | likes | reposts and quotes | views | |
|---|---|---|---|---|---|---|
| Bluesky | 1,039 | 8,236 | 23,127 | 2,380 | ||
| Mastodon | 2,399 | 29,156 | 55,396 | 16,820 | ||
| GitHub | 179 | 5,777 3,520 | 33,866 | 3,317 | ||
| npm | 139 | 1,546 | 75,991,720 | |||
| YouTube | 30 | 1,203 | 32,713 | |||
| Letterboxd | 55 | |||||
| Blog | 20 | |||||
| Hacker News | 59 | 575 | 802 | |||
| All | 4,807 | 37,967 | 114,394 | 22,517 | 76,024,433 |
why do I get the feeling that they’re starting to hard-code answers to these common tests in newer models
Zach Leatherman 7 replies 12 likes Original on Mastodonis this stuff getting better or no
Zach Leatherman 18 replies 25 likes10 reposts Original on Mastodonfollow me for incredibly controversial and spicy takes on software development
Zach Leatherman 42 likes2 reposts Original on Mastodonif you want stable and reliable software, give developers stable and reliable employment
Zach Leatherman 36 replies 701 likes323 reposts4 quotes Original on BlueskyOriginal on Mastodona reliable source has relayed that perhaps the flight attendant in fact said “infant life vests” which, in fairness to my ego, seems equally implausible
look, as my own internal dialogue has surmised: no aircraft can contain an infinite number of life vests. that would be silly. anyone would be silly to think that. the flight attendants did not announce that as part of the safety briefing…
when VC funded projects quiet-quit
Zach Leatherman 3 replies 22 likes2 reposts Original on MastodonOriginal on BlueskyA look back at the year of 11ty, 2025 edition (№8):
+73% releases (×177)
+15% issues closed (×804)
+51% downloads (4.7M)
-28% dependencies (×134)
-22% size (21 MB)
 Build Awesome (11ty) 2 replies 64 likes11 reposts Original on BlueskyOriginal on Mastodon
it clearly needs to be repeated that layoffs are a leadership failure, full stop.
Zach Leatherman 30 replies 195 likes37 reposts3 quotes Original on BlueskyOriginal on Mastodona person who invented a toilet that can flush 50 golf balls watching a commercial from a company advertising a 60-ball flush: “well, shit”
I see a yearly recap blog post, I boost a yearly recap blog post. 💪
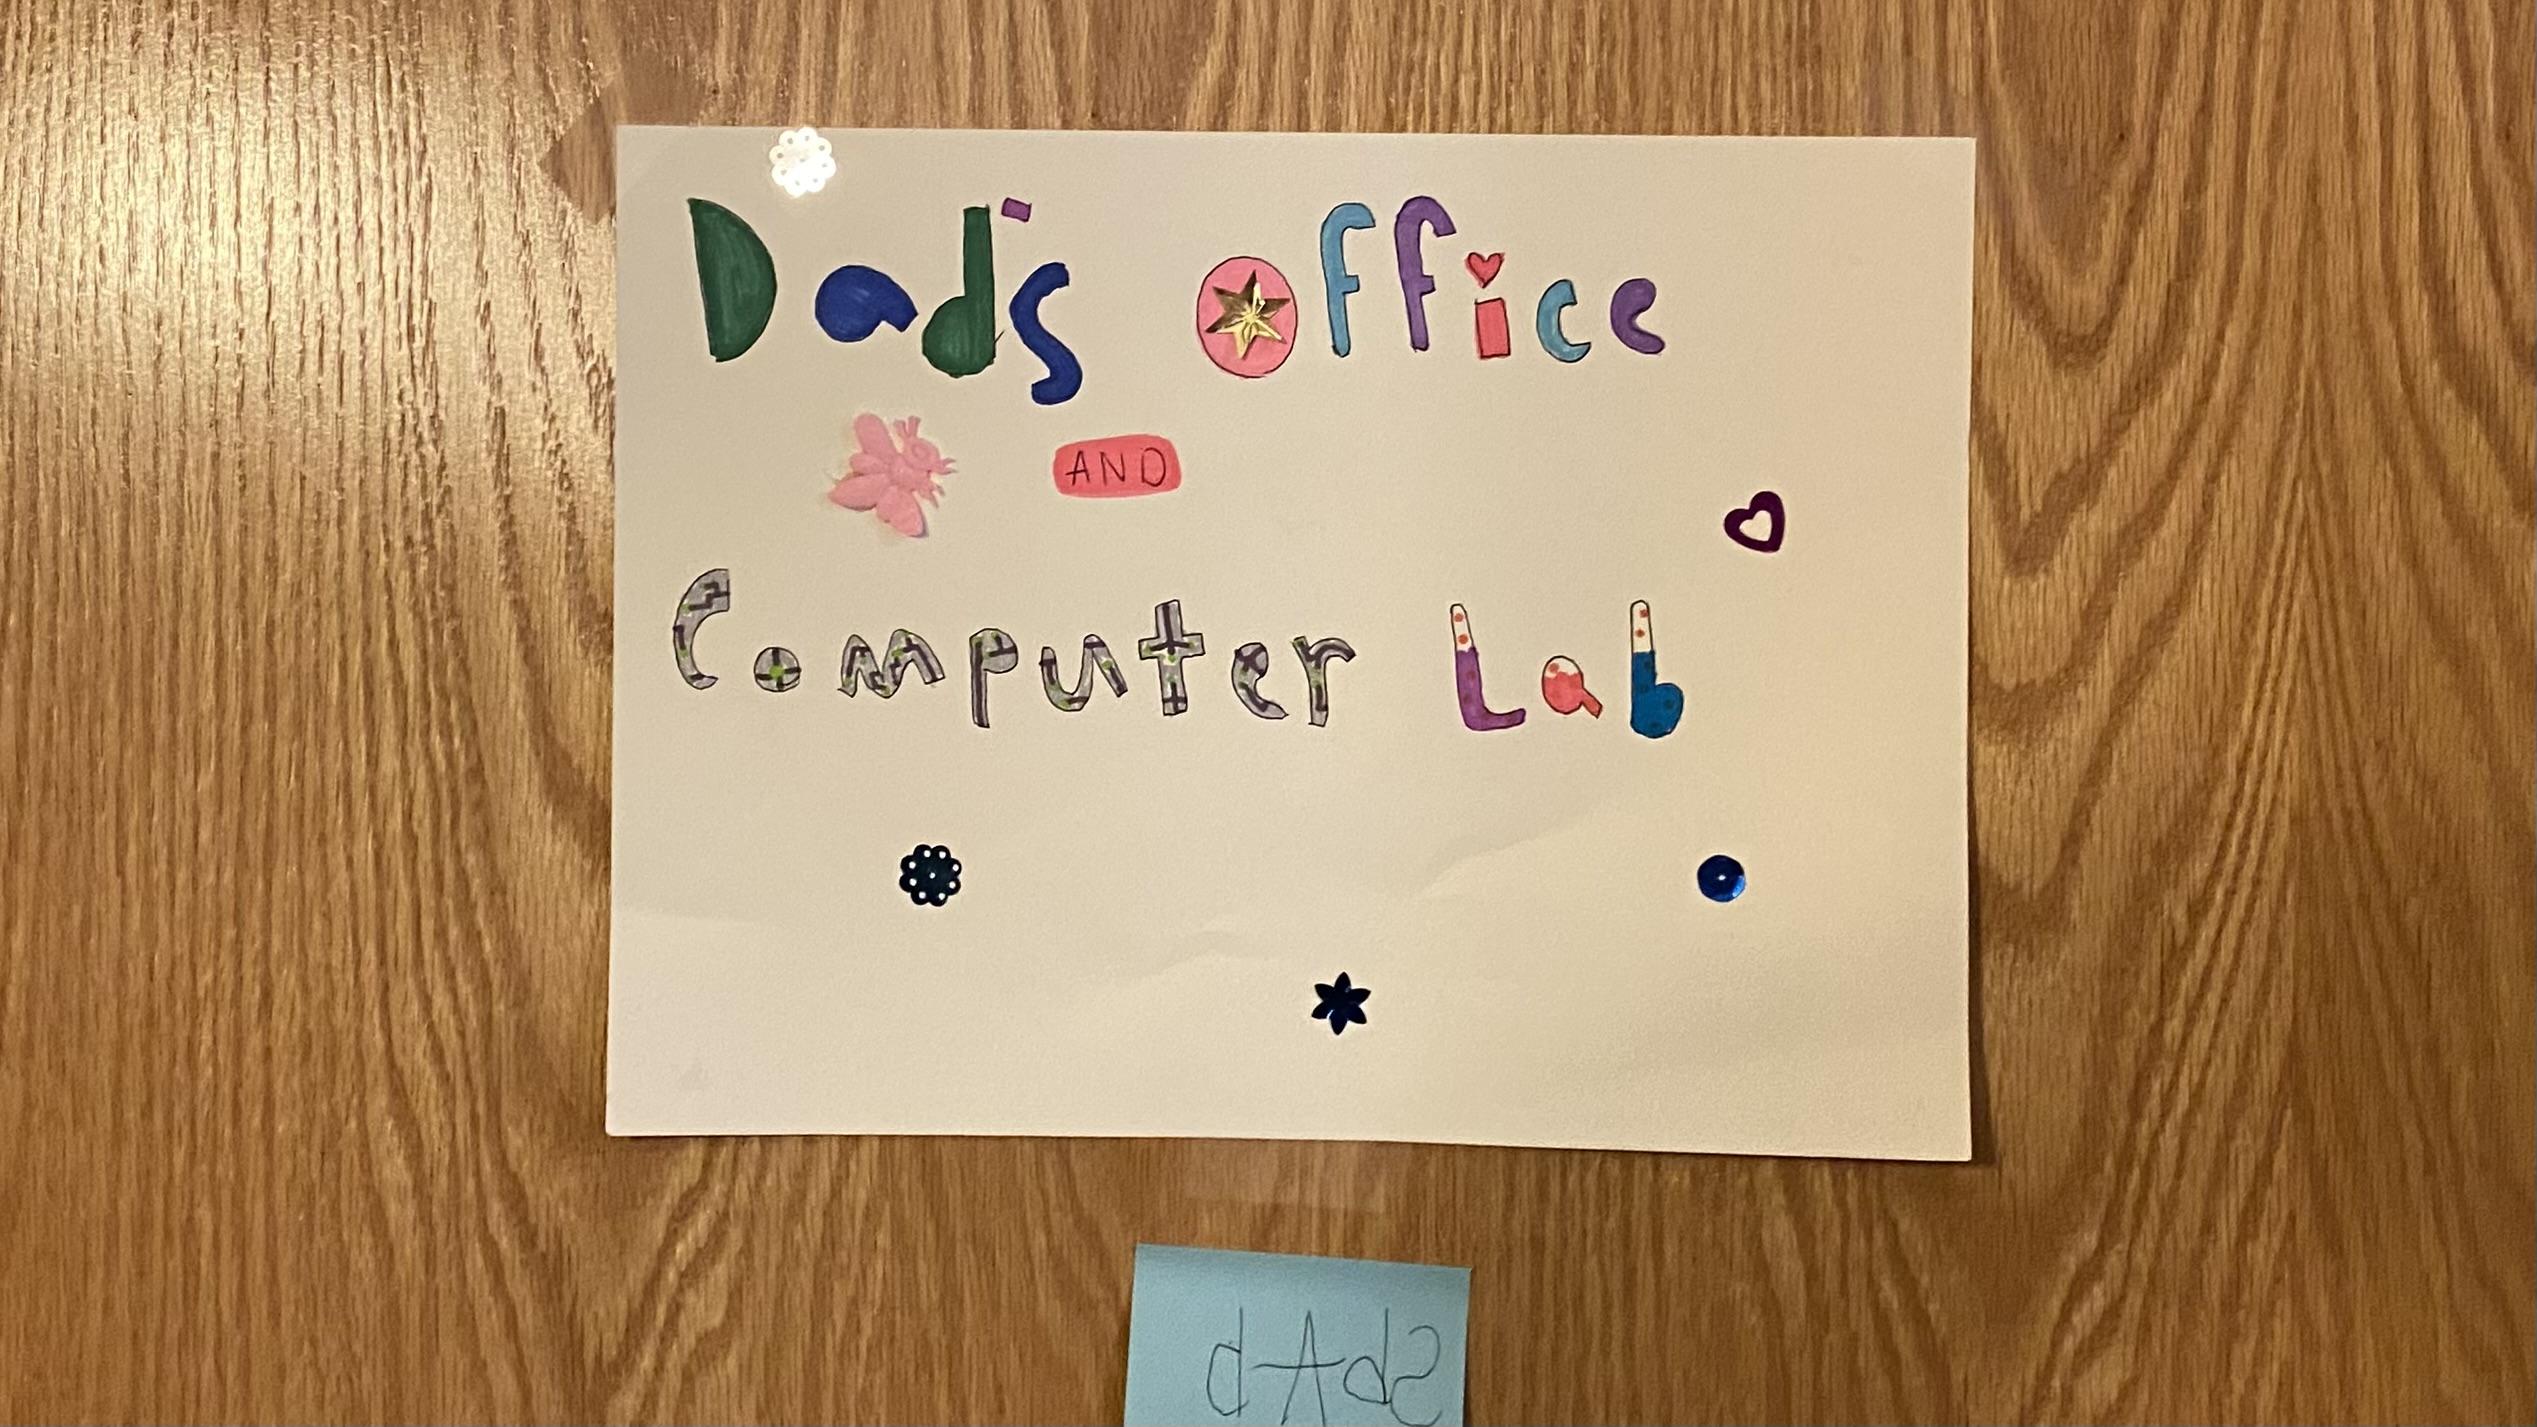
Zach Leatherman 7 replies 11 likes Original on MastodonGot a new sign for my office for Christmas 🎄
Zach Leatherman 58 likes1 repost Original on Mastodonjust to be clear the pluribus hive mind is the borg with a smile
happy holidays
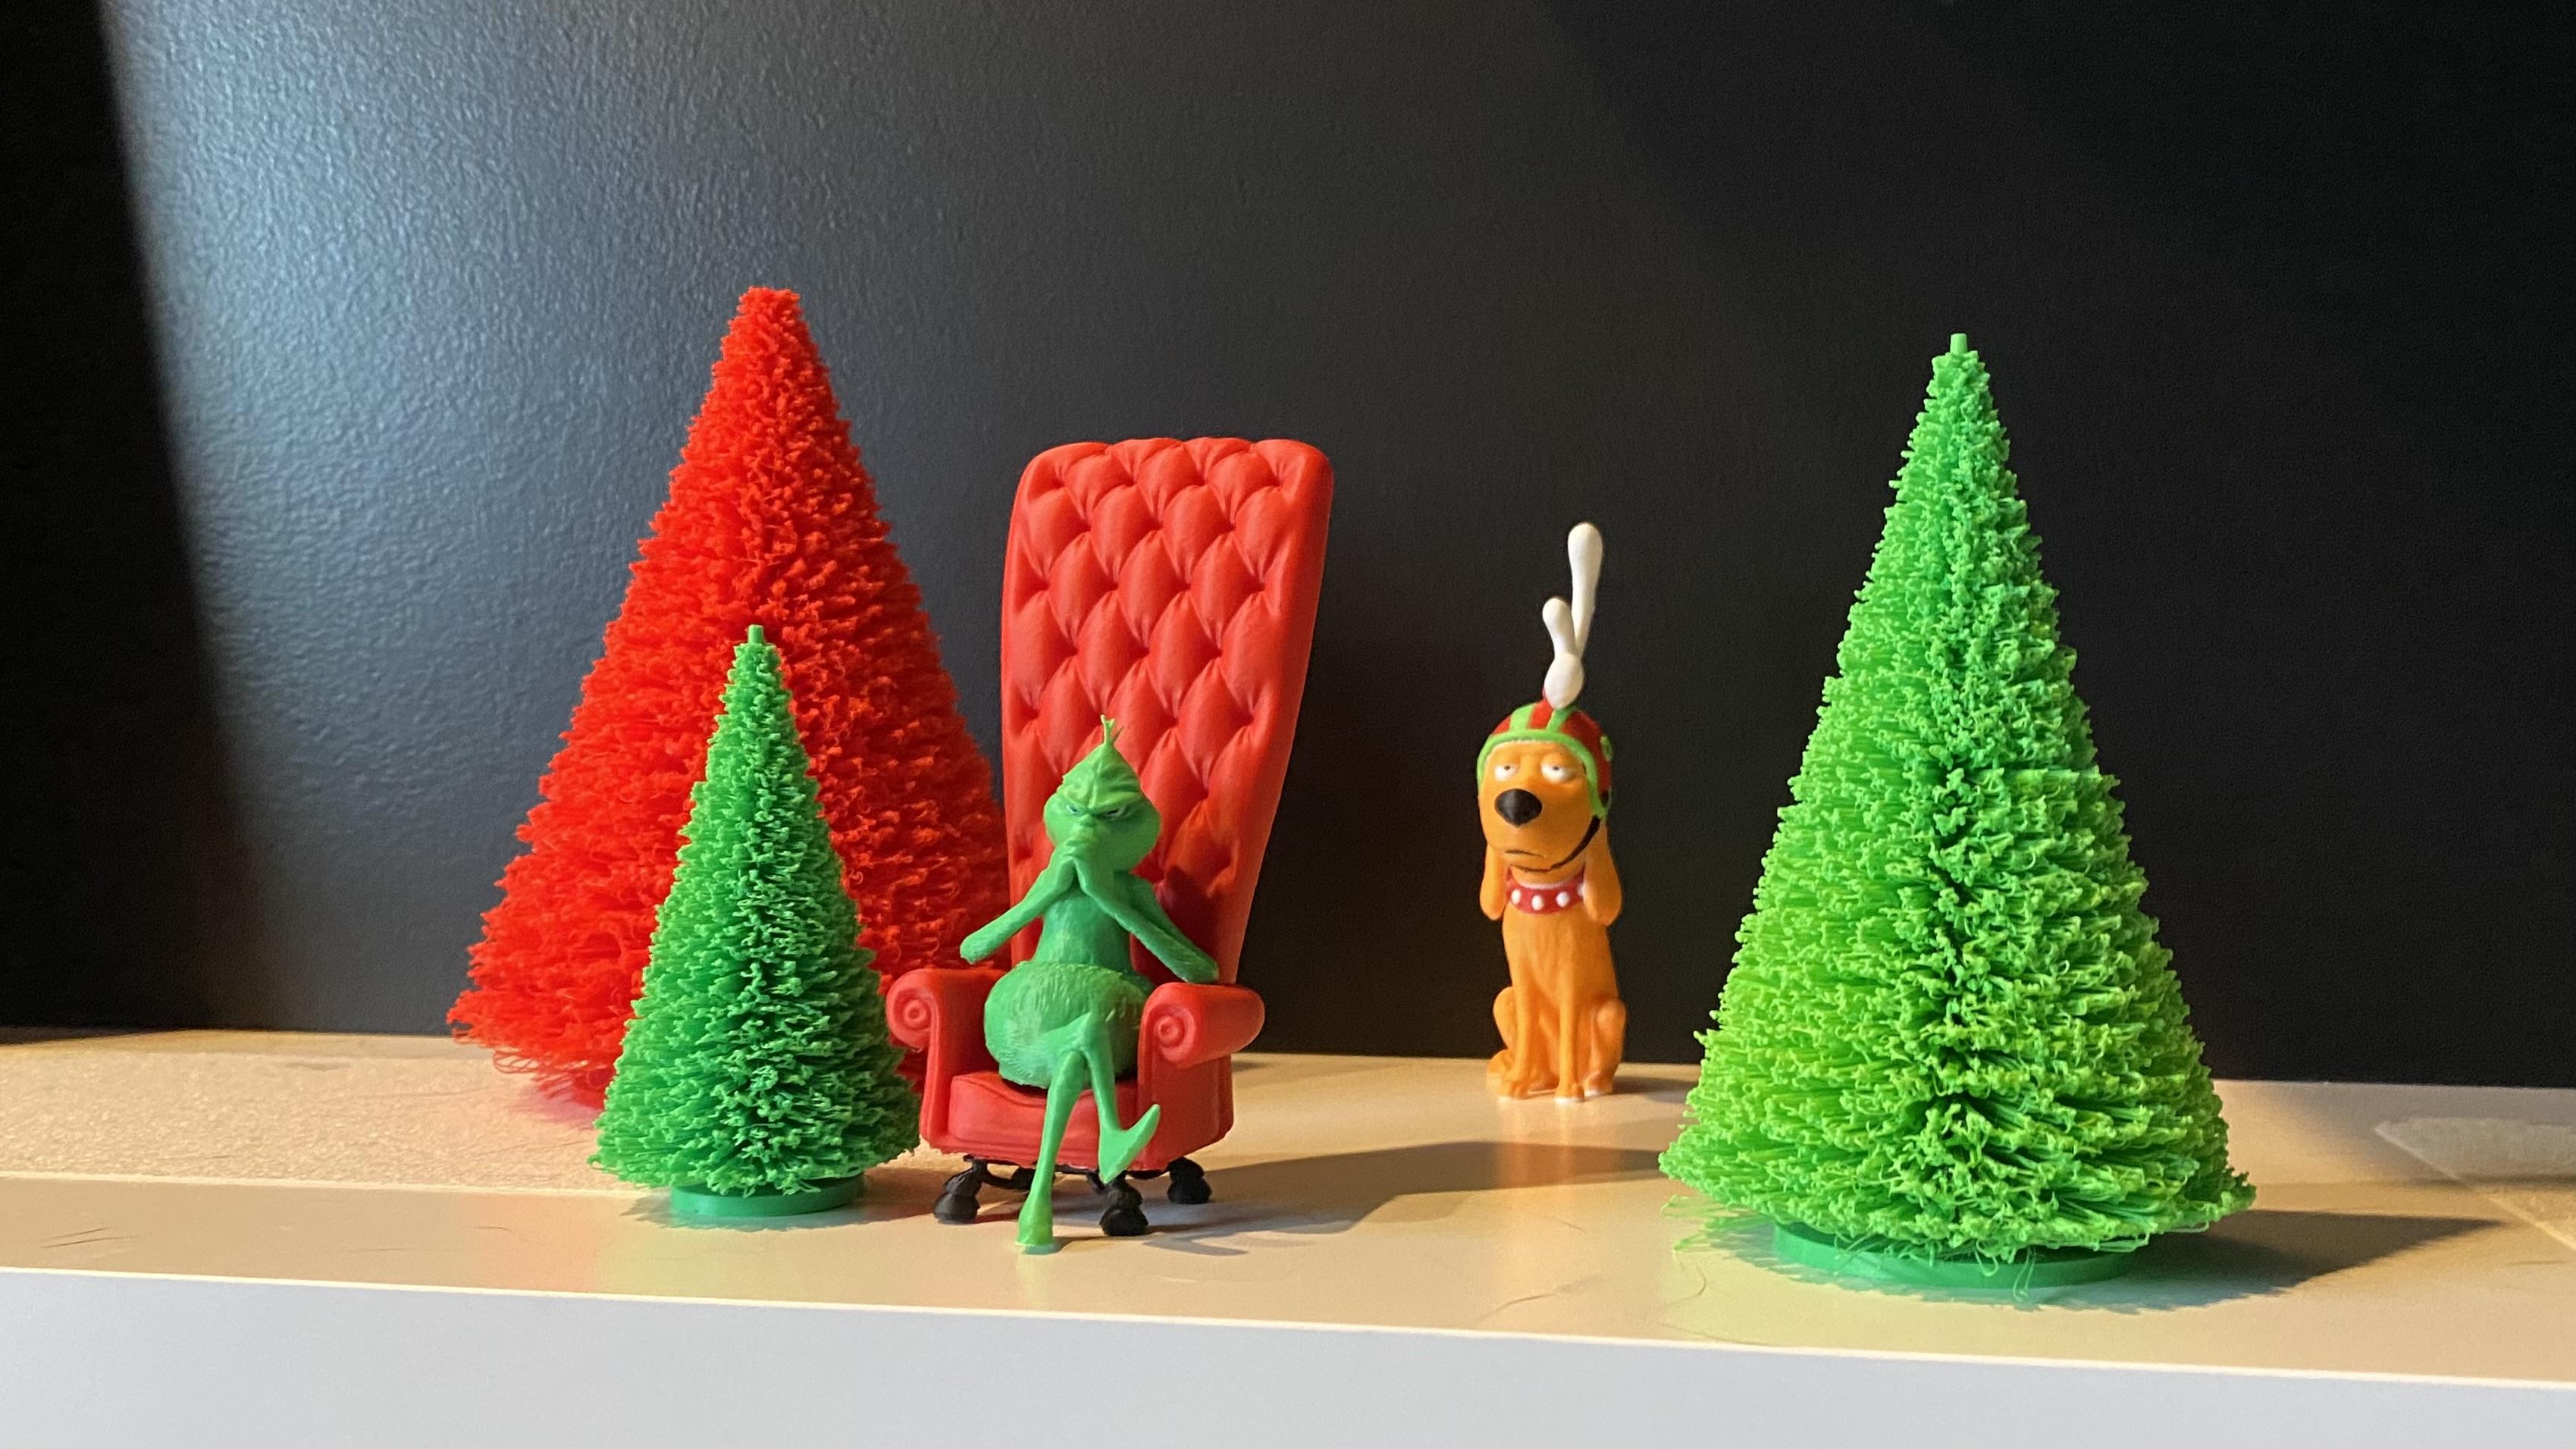
printed our holiday nativity scene this year 🎄
Zach Leatherman 2 replies 32 likes3 reposts Original on Mastodonwith a *huge* assist from Svelte’s https://www.npmjs.com/package/@sveltejs/acorn-typescript here
first draft of zero configuration typescript (with dependency mapping) in @11ty is working — weeeeeeeeeeee
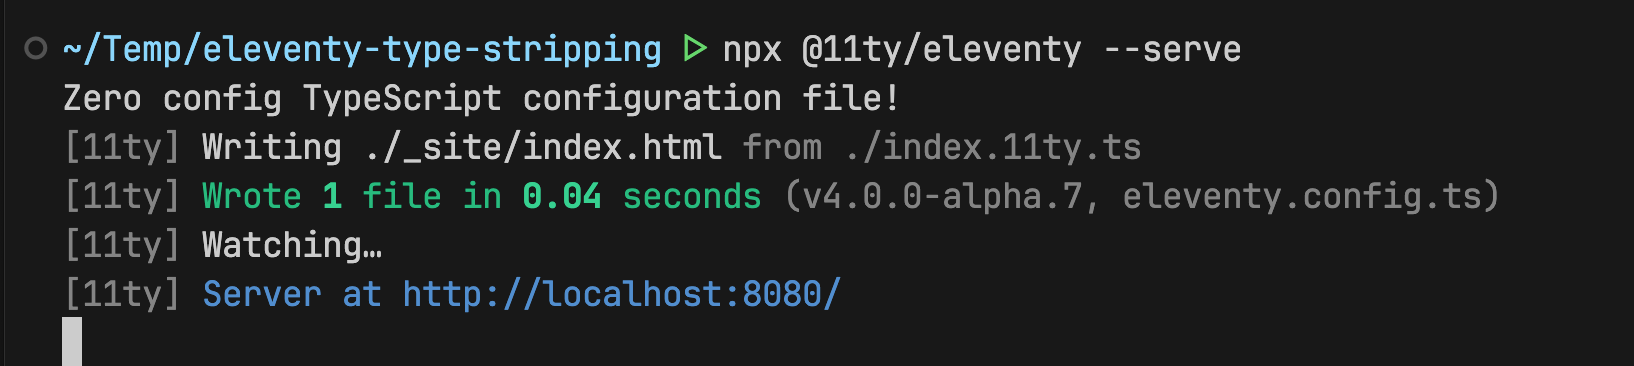
Zach Leatherman 12 replies 47 likes7 reposts Original on MastodonOriginal on Blueskysoftware complexity sells via developer ego
happy holidays!
Zach Leatherman 32 likes4 reposts Original on MastodonOriginal on BlueskyJust deleted a bunch of testing boilerplate in this repo after @vitest added `import.meta.resolve` support 🏆
Zach Leatherman 7 likes1 repost Original on MastodonOriginal on BlueskyI think https://github.com/zachleat/import-module-string is one of the best things I’ve built this year (even if no one else does 😅)
Zach Leatherman 4 replies 20 likes1 repost Original on MastodonOriginal on BlueskyWriting database queries is too close to the metal. Best practices don’t work! It’s time to make SQL enterprise-scale with utility classes.
Zach Leatherman 57 replies 111 likes48 reposts7 quotes Original on MastodonOriginal on BlueskyCurious how to use Node.js’s new Type Stripping feature for TypeScript compatibility with Eleventy? We have you covered: https://www.11ty.dev/docs/languages/typescript/#configuration
Build Awesome (11ty) 8 likes5 reposts Original on MastodonOriginal on Blueskyif you see https://scraper.buffer.com/debugger can you tell them I have beef with them
a one-way street can also be a two-way street with the right attitude
Zach Leatherman 12 replies 14 likes1 repost Original on BlueskyOriginal on Mastodon“a one-way mirror, also called two-way mirror…” — https://en.wikipedia.org/wiki/One-way_mirror
Zach Leatherman 18 replies 15 likes1 repost Original on BlueskyOriginal on MastodonWatched 12 Angry Men last night and it had me wondering if it was legal in the USA in 1957 for women to serve on a jury — looks like it was state-by-state starting with Wyoming in 1870 all the way up to Mississippi in 1968.
Zach Leatherman 2 replies 6 likes3 reposts Original on MastodonCommonJS? ESM? TypeScript? Wait, even CommonJS TypeScript?? Eleventy can run them all.
https://www.11ty.dev/docs/cjs-esm/
Which should you choose? It depends! The social-media sized answer is: ESM 😅
Build Awesome (11ty) 2 replies 19 likes4 reposts Original on BlueskyOriginal on Mastodonleadership wants an everything app
users want an everything bagel
Zach Leatherman 8 replies 45 likes2 reposts1 quote Original on BlueskyOriginal on MastodonTiny bug fix release of `<table-saw>`: https://github.com/zachleat/table-saw/releases/tag/v1.0.7
RE: https://chaos.social/@FlohEinstein/115727872442211456
Y’all are too wild 😅
Zach Leatherman 19 likes3 reposts Original on Mastodon👍✅ Runtimes supporting CommonJS and ESM
👎❌ Modules dual publishing both CommonJS and ESM
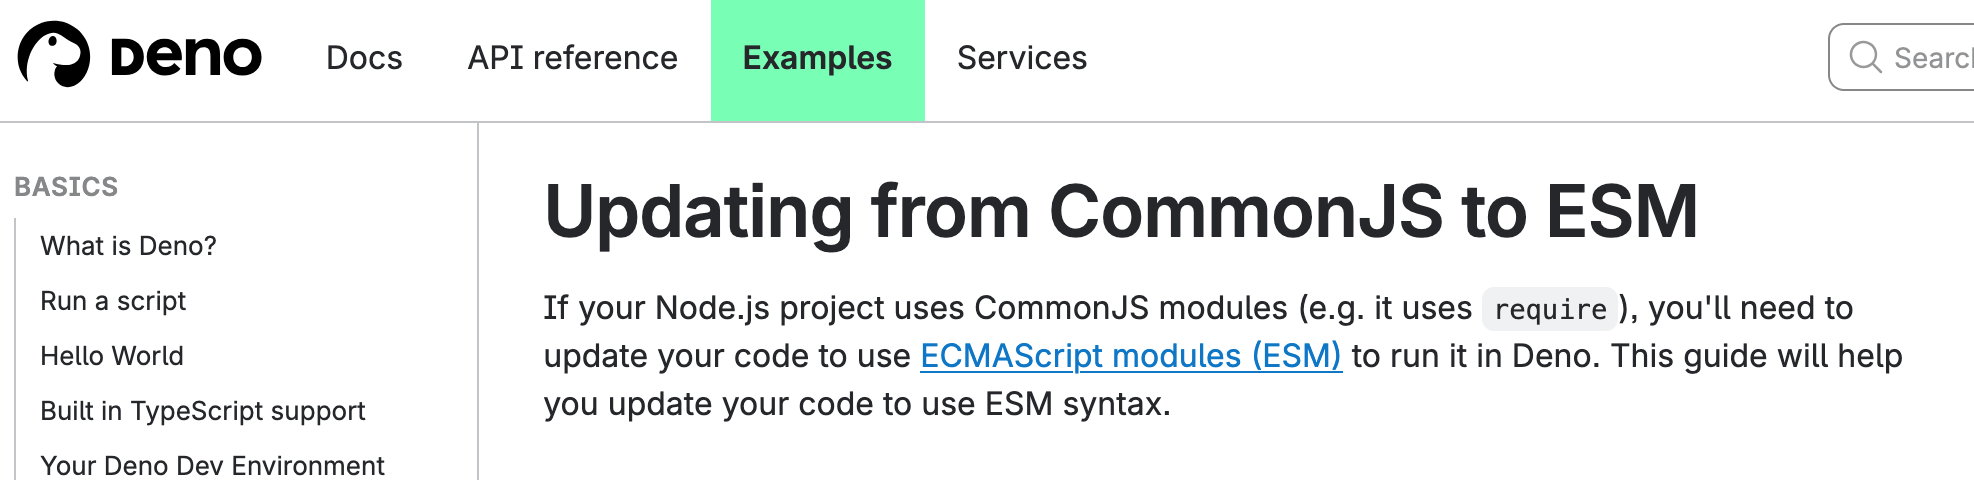
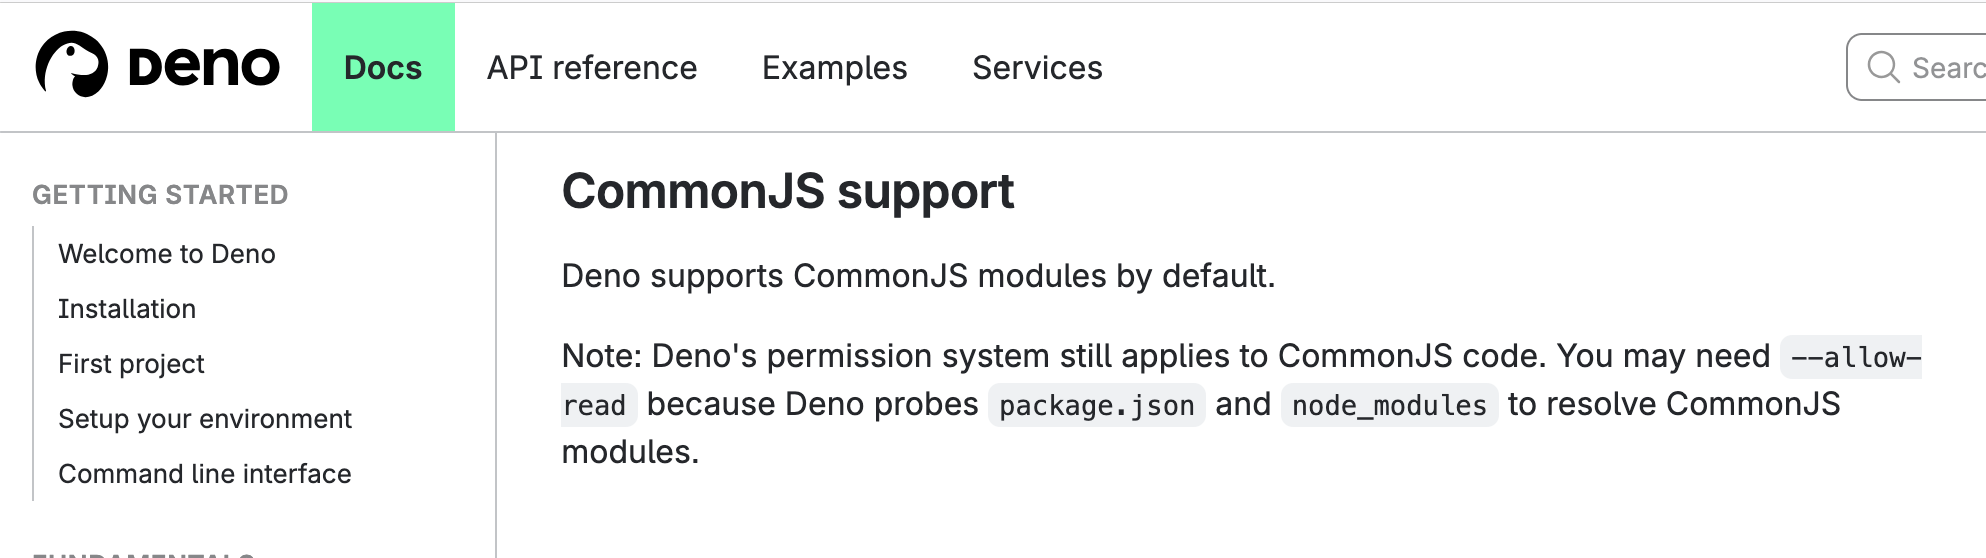
Zach Leatherman 10 likes1 repost Original on MastodonOriginal on BlueskyDeno both supports and absolutely does not support CommonJS 😅
1️⃣ https://docs.deno.com/examples/cjs_to_esm_tutorial/
2️⃣ https://deno.com/blog/commonjs-is-hurting-javascript
3️⃣ https://docs.deno.com/runtime/fundamentals/node/#commonjs-support
a dad hat that says “corny on main”
Zach Leatherman 15 replies 35 likes1 repost Original on MastodonOriginal on BlueskyCurrently wondering what it feels like to work so hard on an open-licensed typeface only to have it co-opted by very terrible and very famous people as part of their core brand identity.
Zach Leatherman 12 replies 40 likes3 reposts Original on MastodonOriginal on BlueskyThankful to @jacklorusso for their 11ty docs contribution detailing how to use @deno_land’s new `dx` command with Eleventy: https://www.11ty.dev/docs/javascript-runtime/#deno
Build Awesome (11ty) 10 likes2 reposts Original on MastodonOriginal on Bluesky*gently opens up the December 15th flap on my react CVE advent calendar*
Zach Leatherman 1 reply 49 likes9 reposts Original on MastodonComing to a canary near you: adding support for Node’s Module Compile Cache feature (existing Node 20+ minimum is unchanged but this is featured tested and available in Node 22.8+ only).
Build Awesome (11ty) 3 replies 3 likes2 reposts Original on MastodonOriginal on Blueskywhat if ___ (good thing) but instead, ___ (worse thing)
one of the 5 stages of grief is denial of service
Zach Leatherman 6 replies 45 likes5 reposts Original on BlueskyOriginal on Mastodonok fine but can react server components show emotional vulnerability too
Zach Leatherman 13 replies 46 likes10 reposts Original on MastodonOriginal on BlueskyEleventy Core Dependency Watch (2025 Edition)
https://www.11ty.dev/blog/dependency-watch/
v4.0.0.alpha.6 (compared with v3) reduces:
1️⃣ dependencies 21.6%
2️⃣ 3rd-party dependencies 27.6%
3️⃣ node_modules weight 33.3%
Build Awesome (11ty) 4 replies 46 likes15 reposts Original on MastodonOriginal on Blueskyis software getting better?
Zach Leatherman 26 replies 13 likes3 reposts Original on MastodonOriginal on BlueskyNew core pre-release: v4.0.0-alpha.6
https://github.com/11ty/eleventy/releases/tag/v4.0.0-alpha.6
Note: this includes a new `@11ty/nunjucks` package.
Build Awesome (11ty) 3 replies 11 likes4 reposts Original on MastodonOriginal on BlueskyI’d like to revise and say that my hotter take is that every VC-funded *open source* software project should report both runway amounts and how many active FTE they have on payroll
Zach Leatherman 3 replies 16 likes2 reposts Original on Mastodonmy hot take is that I think every VC-funded software project should report how much runway they have left every month
Zach Leatherman 8 replies 73 likes13 reposts Original on MastodonOriginal on BlueskyTIL about Carlito, a typeface (derived from Lato) made by Łukasz Dziedzic — the same type designer that made Lato!
Take my npm tokens, take my land,
Take me where I cannot stand.
I don't care, I'm still free,
You can't take the sky from me.
Zach Leatherman 13 replies 40 likes2 reposts Original on BlueskyOriginal on MastodonI wish dependencies would stop embedding their own arguments parser in a package that didn’t need a CLI to begin with.
Eleventy has *three* different dependencies with pretty hefty (and outdated) CLI argument parser libraries 😭
Is there an `overrides`-style feature that works for libraries? (afaik this feature is only for app-level code)
Zach Leatherman 4 replies 15 likes4 reposts Original on Mastodonwe have liftoff
you’re very popular on linkedin (DEROGATORY)
Zach Leatherman 4 replies 24 likes3 reposts Original on Mastodonif you’re cold, your dependency is cold — bring them inside
Zach Leatherman 4 replies 15 likes3 reposts Original on MastodonI don’t know if this is a good decision but it also feels long overdue
Zach Leatherman 56 replies 66 likes14 reposts Original on MastodonStrangers by Spring is #BuiltWithEleventy by @henry and @redintheshell 🏆🏆🏆
Build Awesome (11ty) 4 replies 10 likes2 reposts Original on BlueskyOriginal on MastodonShe’ll never see this because she’s too healthy to be chronically online but I am so thankful to my partner — a genuinely incredible person that I am so happy and privileged to be married to for the last 16 years.
Every truly great thing I have in my life is because of her and every good thing I’ve been given credit for in my life is also because of her.
Only 34 years left until our 50th anniversary ❤️
Zach Leatherman 8 replies 91 likes Original on MastodonNew core pre-release: v4.0.0-alpha.5
Full release notes: https://github.com/11ty/eleventy/releases/tag/v4.0.0-alpha.5
Build Awesome (11ty) 20 likes7 reposts Original on BlueskyOriginal on Mastodontfw your web site is static
Zach Leatherman 21 replies 275 likes46 reposts Original on BlueskyOriginal on MastodonReact has taken down Cloudflare twice now so is this a good time to talk about Enterprise scale or is it still too soon
Zach Leatherman 2 replies 35 likes11 reposts Original on Mastodonif you look in the footer of https://blog.fontawesome.com/ and tap on the Font Awesome flag you’ll see a variant of this component made to work with Font Awesome icons (and reusing the colors from the header image of the blog post too: https://blog.fontawesome.com/blog-awesome-to-11ty/#colors) 🥰
Zach Leatherman 1 reply 5 likes1 repost Original on MastodonOriginal on Bluesky📮🔒 New post on the blog:
Securely publishing our packages to npm
Build Awesome (11ty) 3 replies 12 likes6 reposts Original on BlueskyOriginal on MastodonIt’s decorative <snow-fall> season, friends: https://www.zachleat.com/web/snow-fall/
Zach Leatherman 18 replies 40 likes14 reposts Original on BlueskyOriginal on MastodonMaintenance update: to simplify our docs footprint (and in reaction to deployment retention policies), we will maintain historical versioned branches of our docs for *major* versions only:
https://v2.11ty.dev/
https://v1.11ty.dev/
https://v0.11ty.dev/
Previously hosted minor version subdomains (e.g. https://v0-12-0.11ty.dev) will redirect to their respective major version.
Appreciate y’all!
Build Awesome (11ty) 3 replies 21 likes4 reposts Original on MastodonOriginal on BlueskyDNS stands for “DO NOT meSs with this or you’re going to have a bad time”
Zach Leatherman 4 replies 43 likes4 reposts1 quote Original on MastodonOriginal on Bluesky📮🔒 New post on the blog
No more tokens! Locking down npm Publish Workflows
https://www.zachleat.com/web/npm-security/
Includes a checklist of 8 important things you can do to improve your security footprint when using GitHub and npm.
Zach Leatherman 16 replies 42 likes22 reposts Original on MastodonOriginal on BlueskyFor interested folks, here’s the React PR that fixes CVE-2025-55182 affecting React Server Components (CVSS 10.0 Critical Severity): https://github.com/facebook/react/pull/35277
Blog post: https://react.dev/blog/2025/12/03/critical-security-vulnerability-in-react-server-components
> Even if your app does not implement any React Server Function endpoints it may still be vulnerable if your app supports React Server Components.
Zach Leatherman 3 likes4 reposts Original on MastodonTIL about https://jsx.lol/ from @db which seems to be carrying the torch forward from my blog post a few years back: https://www.zachleat.com/web/react-criticism/
Zach Leatherman 2 replies 13 likes4 reposts Original on MastodonI wanted to do this for an @11ty conference but haven’t had the bandwidth yet 🫠
Zach Leatherman 7 likes1 quote Original on BlueskyOriginal on MastodonFree idea:
A developer conference (née job fair) where all of the speakers are folks that aren’t employed and are looking! Speakers would really benefit from the authority that conference speaking provides and employers looking to hire can send their own devs in to learn (and recruit)!
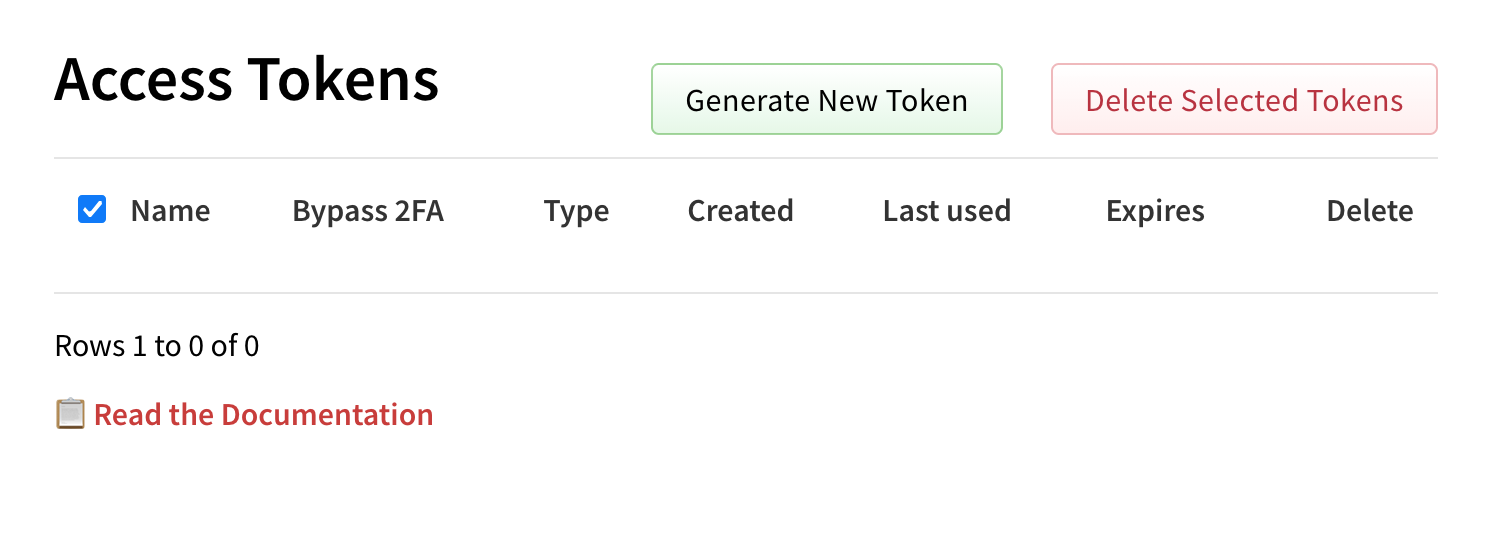
Zach Leatherman 33 replies 93 likes5 reposts2 quotes Original on BlueskyOriginal on MastodonAs a security precaution I had previously configured every single 11ty repository to have its own single-package-scoped npm token (there were probably ~30 or so), so this is a lovely improvement 😅
This took a lot of tedious work but I’m now npm token free, weee!
The @11ty ecosystem is now using Trusted Publishers (https://docs.npmjs.com/trusted-publishers)
Zach Leatherman 14 replies 74 likes11 reposts Original on MastodonOriginal on Blueskytoday I woke up excited to do business excellence
Zach Leatherman 7 replies 13 likes1 repost Original on MastodonI have been informed (via email) that Zach Leat has been nominated for the Business Excellence Awards 2026 — please clap 😅
The @smashingmag Email Newsletter on Web Performance this week was great!
This year we’re thankful for everyone that took a few minutes to fill out our 8 question survey (with 5 multiple choice questions 😅).
If you haven’t yet, we are still accepting submissions! It will help us prioritize the future of our project! Appreciate y’all!
Build Awesome (11ty) 12 likes11 reposts Original on MastodonOriginal on Blueskyfor black friday I took 20% of the words off of my blog but I won’t tell you which ones
Zach Leatherman 2 replies 28 likes1 repost Original on BlueskyOriginal on MastodonUpdate: at time of writing Eleventy core (0.x, 1.x, 2.x, 3.x, 4.x prereleases) and our official plugins are still unaffected.
(Compromised package count was updated to 834 from 533 in the latest @SocketSecurity update: https://socket.dev/blog/shai-hulud-strikes-again-v2)
Build Awesome (11ty) 3 replies 9 likes6 reposts Original on MastodonIs there a way to configure an npm package to *require* provenance and fail any publish attempts that don’t have it? I don’t think the Trusted Publisher stuff has that option, if I’m reading it correctly.
Was wondering how to use Subresource Integrity with dynamic import() — thought maybe there was a path forward using import attributes (no) but I did stumble across this excellent post about using it with Import Maps (from @guybedford):
Zach Leatherman 11 likes6 reposts Original on MastodonOriginal on BlueskyHow to hallucinate using Web Components https://www.zachleat.com/web/hallucinate/
Zach Leatherman 6 replies 16 likes1 repost Original on BlueskyOriginal on Mastodonparticipating in the JavaScript ecosystem continues to feel like living in a house that’s on fire and all of your roommates are just buying their own fire extinguishers and pretending that it’s just a temporary bout of really hot weather
Zach Leatherman 25 replies 101 likes25 reposts Original on BlueskyOriginal on MastodonThere is an active npm security event: https://socket.dev/blog/shai-hulud-strikes-again-v2
At time of writing, Eleventy core and our official suite of plugins are unaffected.
Build Awesome (11ty) 4 replies 23 likes24 reposts1 quote Original on MastodonThe 80px vertical page shift from “This issue has been moved to a discussion” clunking in on an already loaded page may be my villain origin story.
Bring back toasts, GitHub! 🥸
Zach Leatherman 8 replies 19 likes1 repost1 quote Original on MastodonOriginal on BlueskyI have elevated to a new plane of open source existence
Pretty wild that GitHub Contribution Graphs don’t count responding to or closing issues as Activity (though *opening* issues counts 🥸)
Zach Leatherman 13 replies 19 likes3 reposts Original on Mastodonwe are definitely triaging like we’ve never triaged before
Zach Leatherman 5 replies 23 likes Original on MastodonSORRY FOR THE LATE RESPONSE.
APPRECIATE YOUR PATIENCE.
SORRY FOR THE RESPONSE.
APPRECIATE YOU.
SORRY, RESPONSE.
APPRECIATE.
SORRY.
Zach Leatherman 8 replies 26 likes2 reposts Original on Mastodonthis is using a <squirm-inal> Web Component from 2021: https://github.com/zachleat/squirminal/
2021-vintage Web Components are React 17-era. No big refactors or rewrites required.
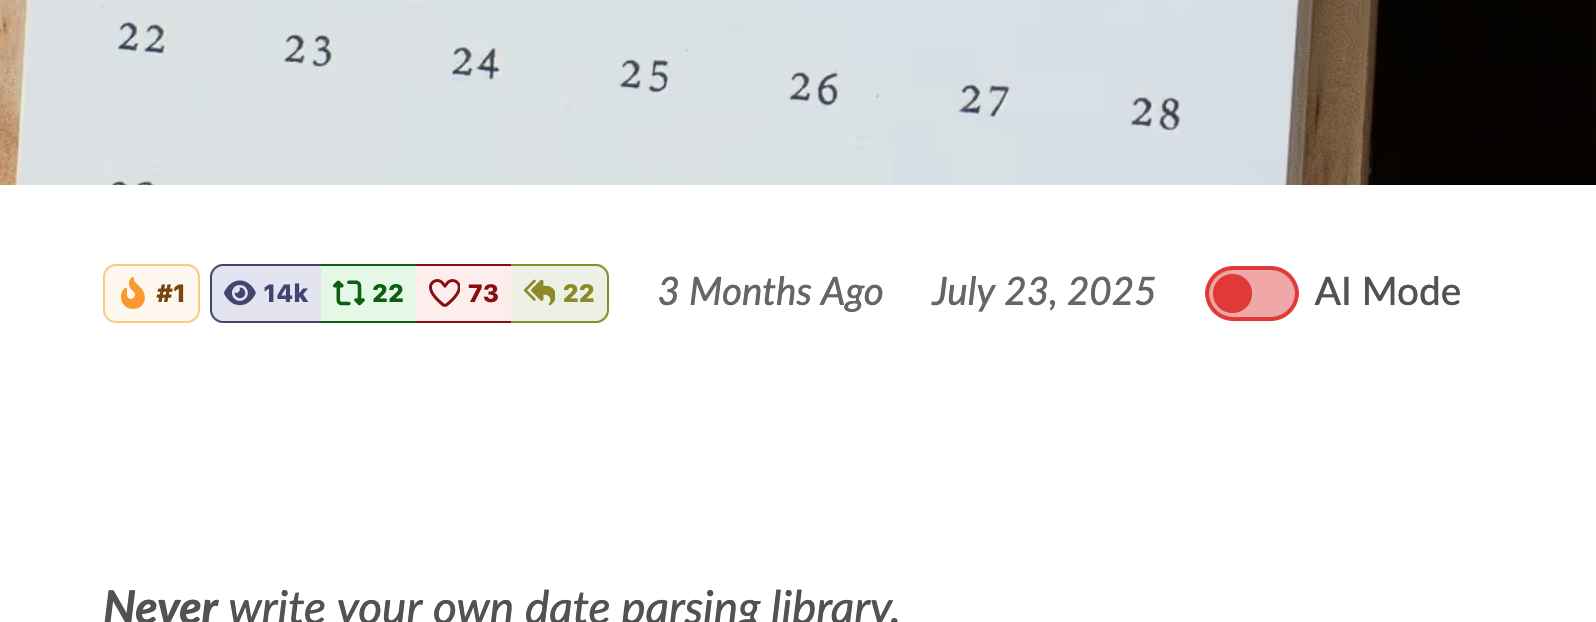
went on a small side quest this morning and added an AI Mode toggle to my blog posts
e.g. https://www.zachleat.com/web/adventures-in-date-parsing/
Zach Leatherman 33 replies 33 likes6 reposts Original on MastodonOriginal on BlueskyHelp guide the future of Eleventy by participating in the Eleventy Community Survey (and Suggestion Box):
Build Awesome (11ty) 7 replies 32 likes34 reposts Original on BlueskyOriginal on Mastodonwe are really leaning into those outages today, huh https://www.githubstatus.com/
Zach Leatherman 8 replies 4 likes1 repost Original on Mastodon@bobmonsour is looking for feedback on https://11tybundle.dev/ — please participate in the redesign survey!
https://docs.google.com/forms/d/e/1FAIpQLSfef-ekQaPHSRnIQY8iUn-fmR79P1BXep-j2jPM3RKCDEcDnw/viewform
Build Awesome (11ty) 3 replies 15 likes12 reposts Original on BlueskyOriginal on MastodonI can track web development eras like tree rings, but each ring is move-fast-and-break-things devs saying “we don’t care about Y and you shouldn’t either—here are a bunch of tools that disregard Y” and indie folks saying “no thanks, I do care about Y—those tools aren’t useful if they don’t take Y into account.”
Later it becomes “as an industry we have always thought Y was very important—we should build *new* tools that embrace Y, I wish someone would have said something before”
Rinse & repeat.
Zach Leatherman 2 replies 33 likes2 reposts Original on MastodonRE: https://infosec.exchange/@jerry/115571012524697515
we should have a cyber-monday-esque international holiday where we turn the web off for an entire day
Zach Leatherman 15 likes1 repost Original on Mastodonyou know what hasn’t taken down Cloudflare (afaik): dangerouslySetInnerHTML
Zach Leatherman 5 replies 11 likes Original on Mastodondid Cloudflare do another React useEffect
Zach Leatherman 10 replies 60 likes2 reposts Original on BlueskyOriginal on Mastodonwhy is no one talking about the <fieldset> of zelda
Zach Leatherman 25 replies 40 likes3 reposts1 quote Original on BlueskyOriginal on MastodonTIL about the HTML Size Analyzer from DebugBear. Great for finding sneaky Data URIs or large payloads of JSON in your pages:
Zach Leatherman 4 replies 41 likes15 reposts Original on MastodonOriginal on Bluesky“are the devtools keeping pace with emerging web standards?” is a very good litmus test for whether a browser vendor is investing alongside the web or just treading water
Zach Leatherman 4 replies 15 likes2 reposts Original on MastodonJeppe Reinhold was kind enough to share this tool from Craigory Coppola to compare popularity of different Major/Minor versions of a package on npm:
Zach Leatherman 3 likes Original on MastodonShipped a tiny little breaking change to <browser-window> this morning to show the full URL in the URL-bar by default (with an escape hatch if you hate it)
Repo: https://github.com/zachleat/browser-window
Demo: https://zachleat.github.io/browser-window/demo.html
Now available in v2.0.0
Zach Leatherman 7 replies 25 likes3 reposts Original on MastodonOriginal on Bluesky