is there really no low-level mechanism to intercept boolean primitive coercion in JavaScript?

why can’t I extend `Boolean` to make `new MyBoolean(false)` be `falsy`? (I understand why it isn’t, but I want to make it so)

> Note: Unlike other type conversions like string coercion or number coercion, boolean coercion does not attempt to convert objects to primitives by calling user methods.

https://developer.mozilla.org/en-US/docs/Web/JavaScript/Reference/Global_Objects/Boolean#boolean_coercion

folks migrating away from hosting providers that hadn’t previously considered how tightly coupled their web framework was to said host are about to learn some things — I’m sorry and I wish you the best on your journey

Make sure you follow @socket.dev to see the latest in JS supply chain security (we’ll update you if any reports affect Eleventy!)

Some good practices to help mitigate in your projects:

1. Use `npm install --ignore-scripts` (or use pnpm)
2. Use `npm ci` and a package-lock.json on your build server

@ricmac do not look this up but it is still live on his web site. He posted naked pictures of his family (including his underage kids? wtf??) on his web site as a “naked christmas card” — surprised he didn’t get in more trouble for it tbh. For as much conversation that goes into influencers posting stuff of their kids before they know what consent is, it’s wild to look back on this

Crashing out at how poorly npm (Microsoft) is handling this security incident. Eleventy is not affected any more but *lots* of other tools in the JavaScript ecosystem are!

Hours later and the compromised package versions are still public…

Maybe don’t install anything from npm today, folks.

Edit: the issue was resolved at approximately 18:30Z

remember: folks that say “we won’t do it without your consent” often also (much more quietly) believe that agreeing to their privacy policy counts as consent

Charlie Brooker crying & throwing up learning that the smart ring users are mad that the smart ring company signed a deal with the United States military & the smart ring company's defense is well have had deals with the DoD forever & we won't share ur smart ring data with them, unless u r a troop

What Oura Ring’s partnership with the U.S. military means for your data
Oura Ring promises users their data is safe — is that enough?

— Erin Fogg says Free Link (September 3, 2025 at 8:59:48 PM UTC)

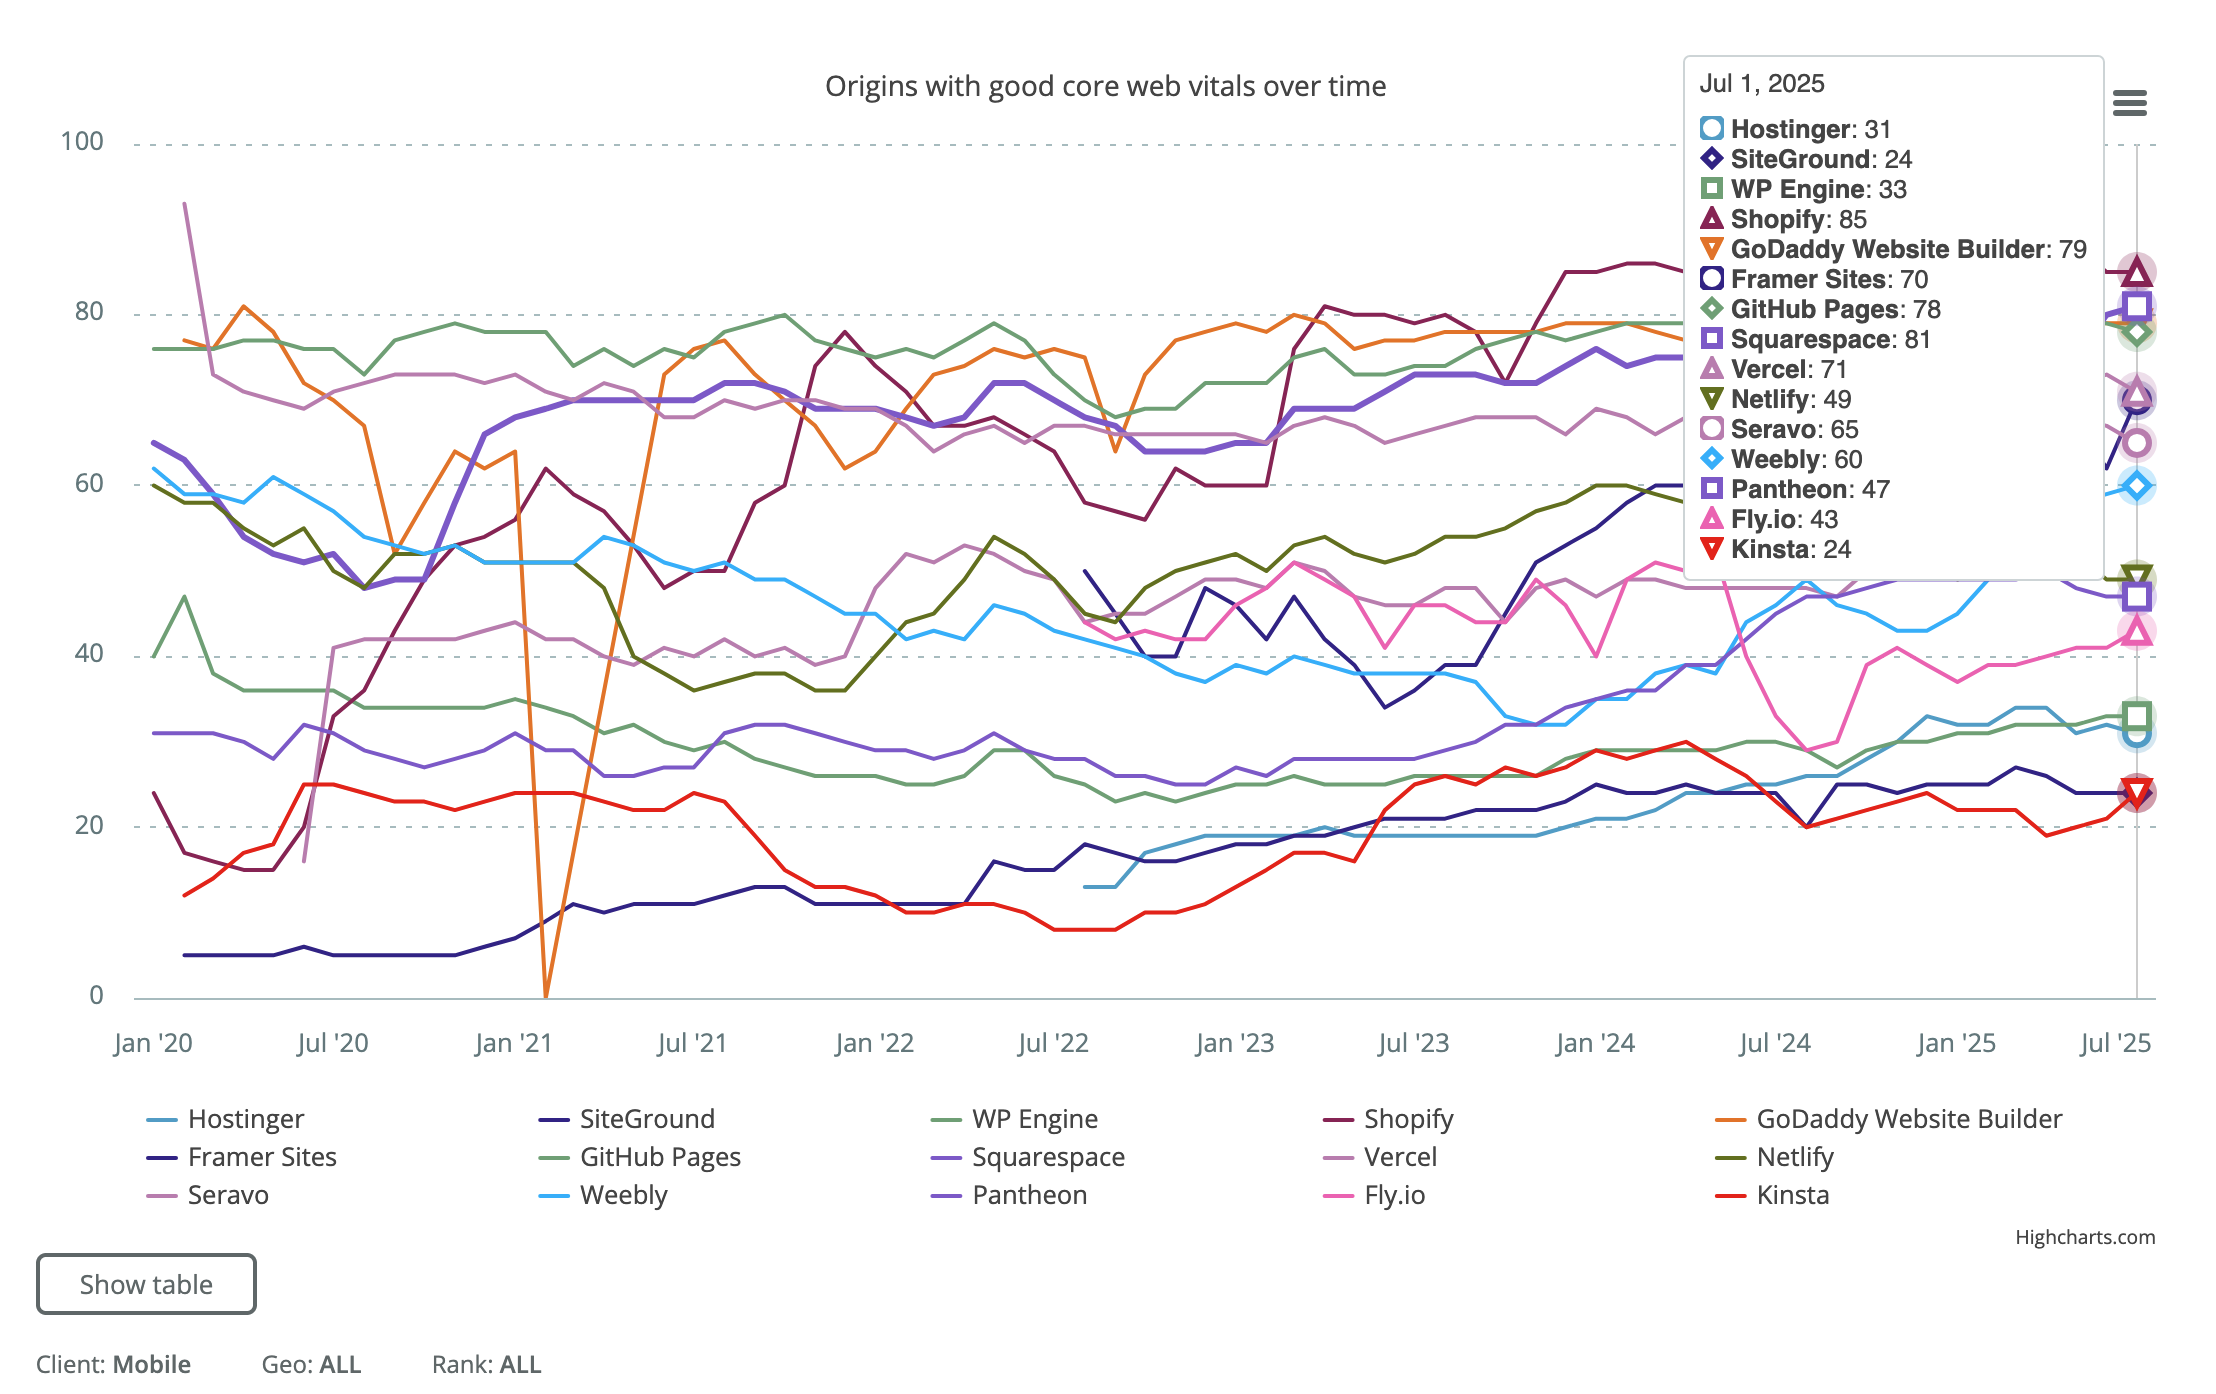
Intuitively, these charts might tempt you to compare these hosts, making assumptions about the investment each of these services put into their server infrastructure — but that wouldn’t be the whole story.

Knowing that TTFB is both server AND client-dependent (including times for Service Worker init, DNS, TLS), this graph might instead represent how wealthy each service’s audience is.

Looks like the above was last updated in November 2024 but links to the HTTP Archive Tech Report for newer data: https://httparchive.org/reports/techreport/tech?good-cwv-over-time=TTFB&tech=Hostinger,SiteGround,WP+Engine,Shopify,GoDaddy+Website+Builder,Framer+Sites,GitHub+Pages,Squarespace,Vercel,Netlify,Seravo,Weebly,Pantheon,Fly.io,Kinsta&geo=ALL&rank=ALL#comparison-good-cwvs

Here’s a screenshot from 01 July 2025:

Screenshot of the HTTP Archive Tech Report showing Shopify and Squarespace still occupying the top two spots in TTFB Core Web Vitals performance at 85% and 81% respectively