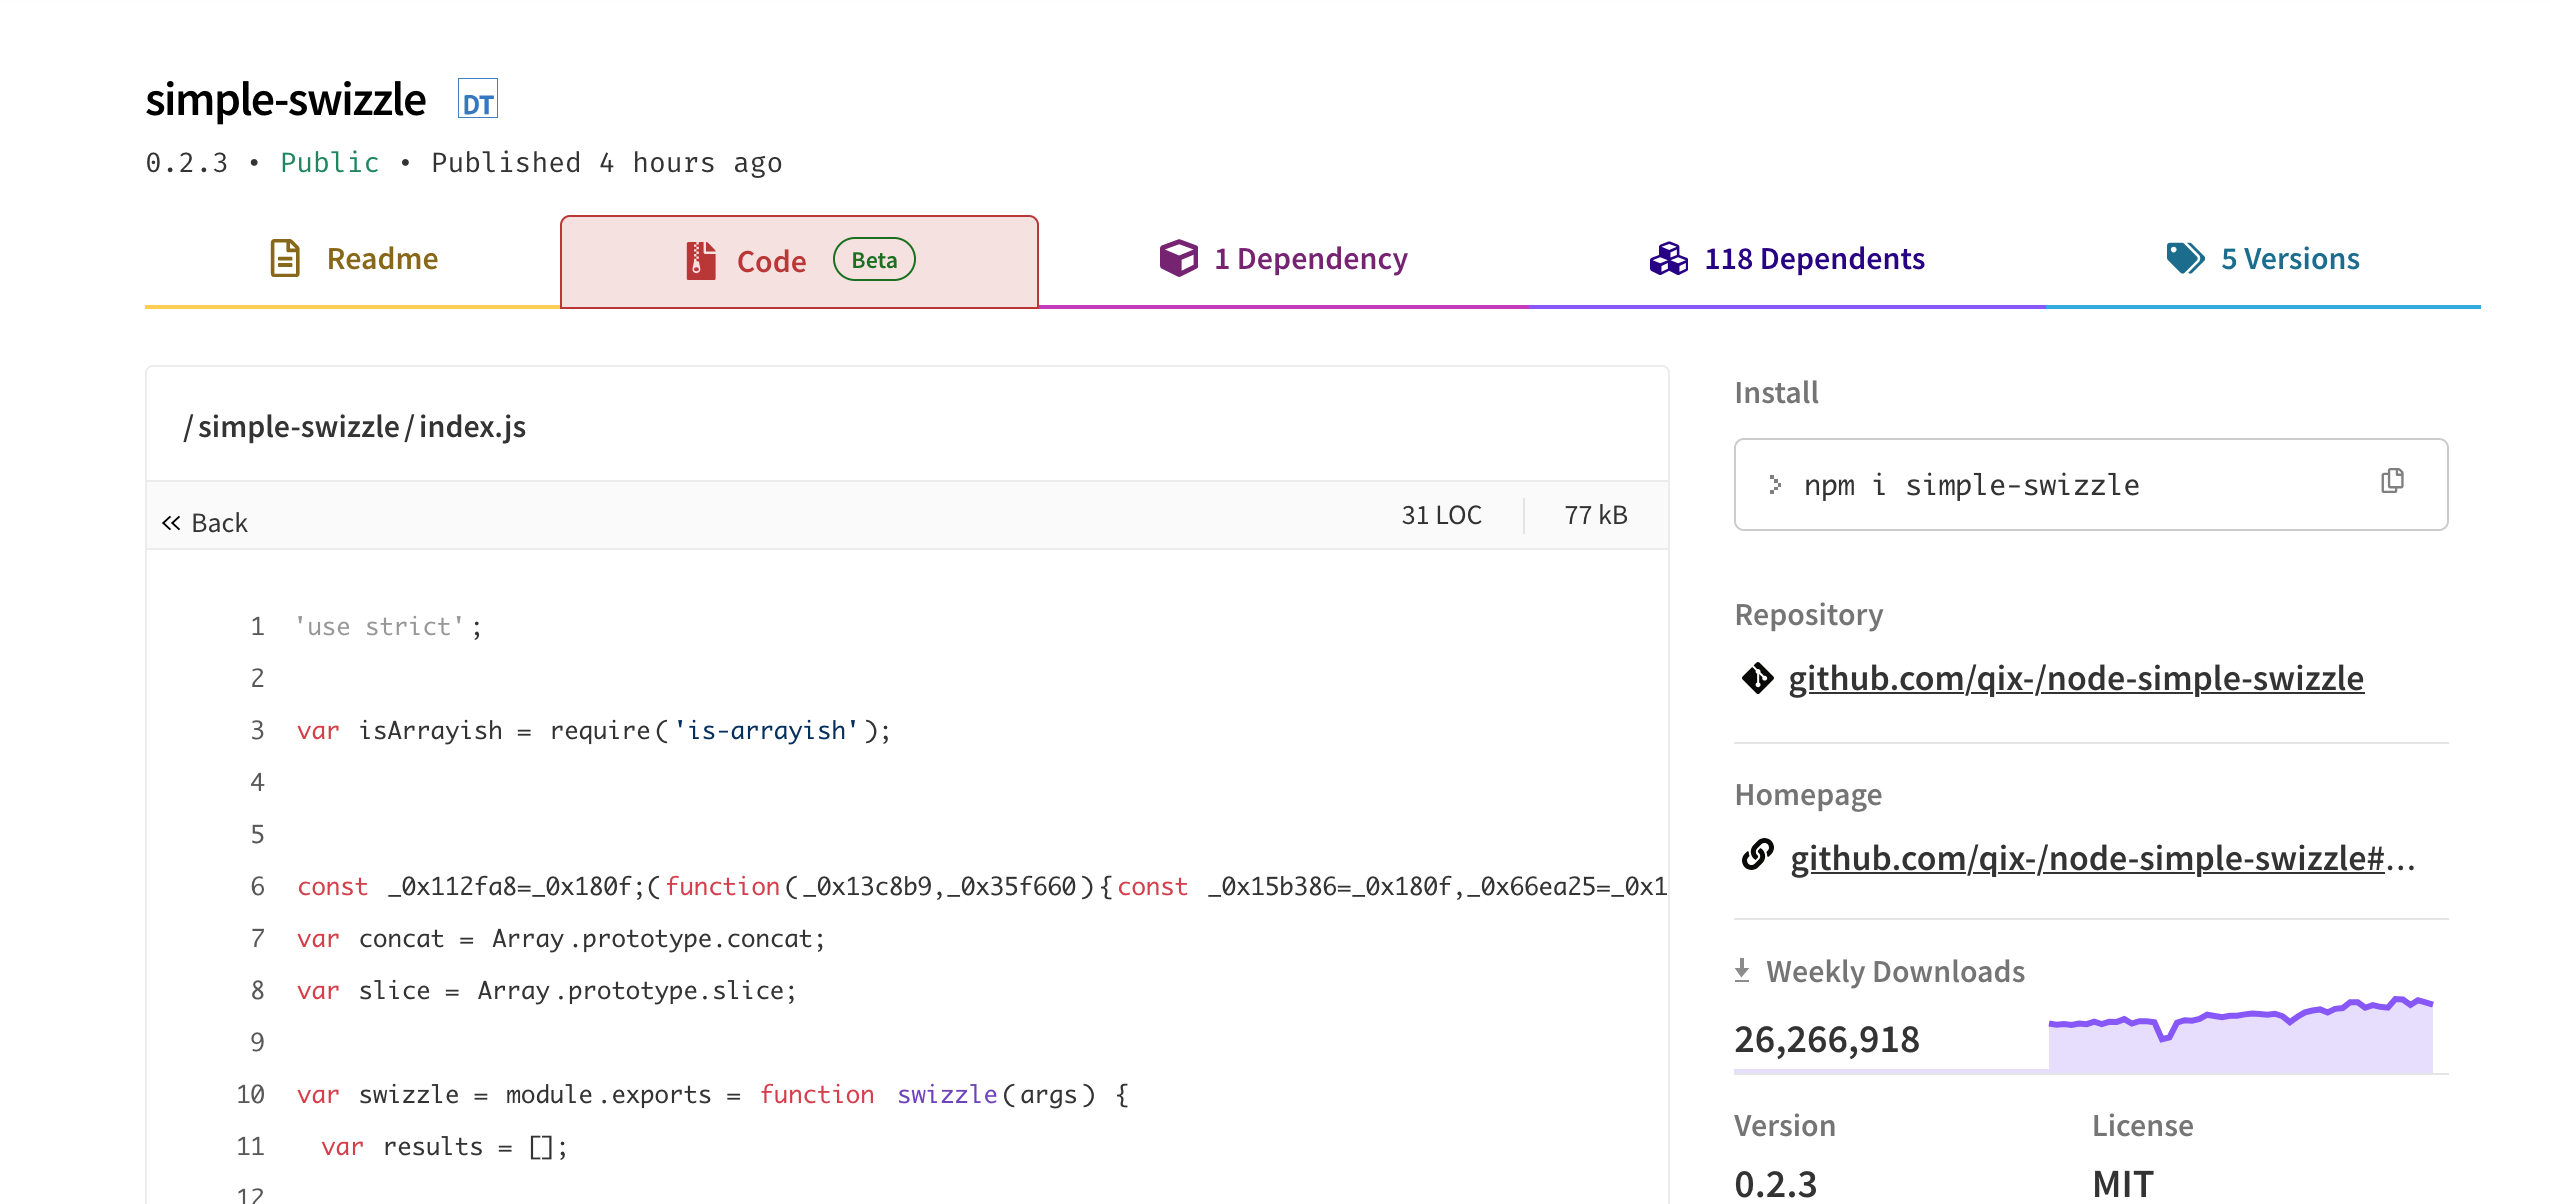
simple-swizzle@0.2.3 is *still* public, active, and in the wild. You can see the malicious code on the code browser: https://www.npmjs.com/package/simple-swizzle/v/0.2.3?activeTab=code
Edit: seeing folks boost this one still but editing to say that it’s been resolved
 Zach Leatherman 12 replies 16 likes7 reposts Original on Mastodon