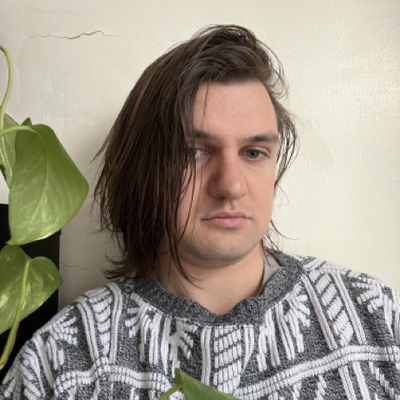
Why does socket.dev report that the latest version of next.js has a malware dependency? https://socket.dev/npm/package/next/alerts/15.2.3?tab=dependencies
“Malicious code in gen-mapping (npm) Any computer that has this package installed or running should be considered fully compromised.”
Update: looks like this is a pretty big flaw in the vulnerability scanner — not in next (check the replies for more info)

19 replies
@zachleat auth0 just sent me a CVE about their NextJS because we use their nextjs-auth0 package 😬 https://sec.okta.com/articles/nextjs-CVE-202529927/
@chrisw_b ah, yeah — I saw some discussion about that! That’s why I went to socket to look at the reports, but this seems unrelated?
@zachleat oh yeah, you're right! sorry I didn't actually finish reading everything first- looks like it's just a mistake though; someone squatting a non-scoped version of the same package: https://github.com/jridgewell/gen-mapping/issues/12
@chrisw_b whoa, this is a *wild* mistake by the socket team then? They’re reporting every single version of this package as malware
@zachleat yeah I'm guessing they use this tool, and I'm baffled that this would go unaddressed so long? https://github.com/anchore/grype/issues/1701
name squatting has been an issue with npm forever, telling scoped packages and non scoped apart feels essential?
@chrisw_b WOW.
@zachleat https://github.com/vercel/next.js/security/advisories/GHSA-f82v-jwr5-mffw
EDIT: Oh shit no, that's a different major issue. Yikes.
@zachleat Diving into it now. It seems that socket.dev sources its info from osv.dev, which claims the package has embedded malicious code. Not sure where that is coming from.
- https://test.osv.dev/vulnerability/MAL-2022-3326
- https://cwe.mitre.org/data/definitions/506.html@timsev someone linked me to https://github.com/jridgewell/gen-mapping/issues/12 which seems to suggest a `gen-mapping` report from 2022 is being misattributed to this namespaced package
@zachleat Ah, that could explain things!
-
Update: thanks to @chrisw_b for hunting this down: looks like a huge flaw in the vulnerability scanner being used by these tools (it ignores namespaces on package names!)
More info:
https://github.com/jridgewell/gen-mapping/issues/12
https://github.com/anchore/grype/issues/1701-
it’s hard not to be jaded when facial recognition is being used in criminal investigations while our industry is having trouble accurately testing whether two strings are equal
The @SocketSecurity folks have quickly fixed this one:
Another update: the socket.dev folks fixed this on their end almost immediately but this has now also been fixed upstream in `grype` too: https://github.com/anchore/grype/issues/1701
-