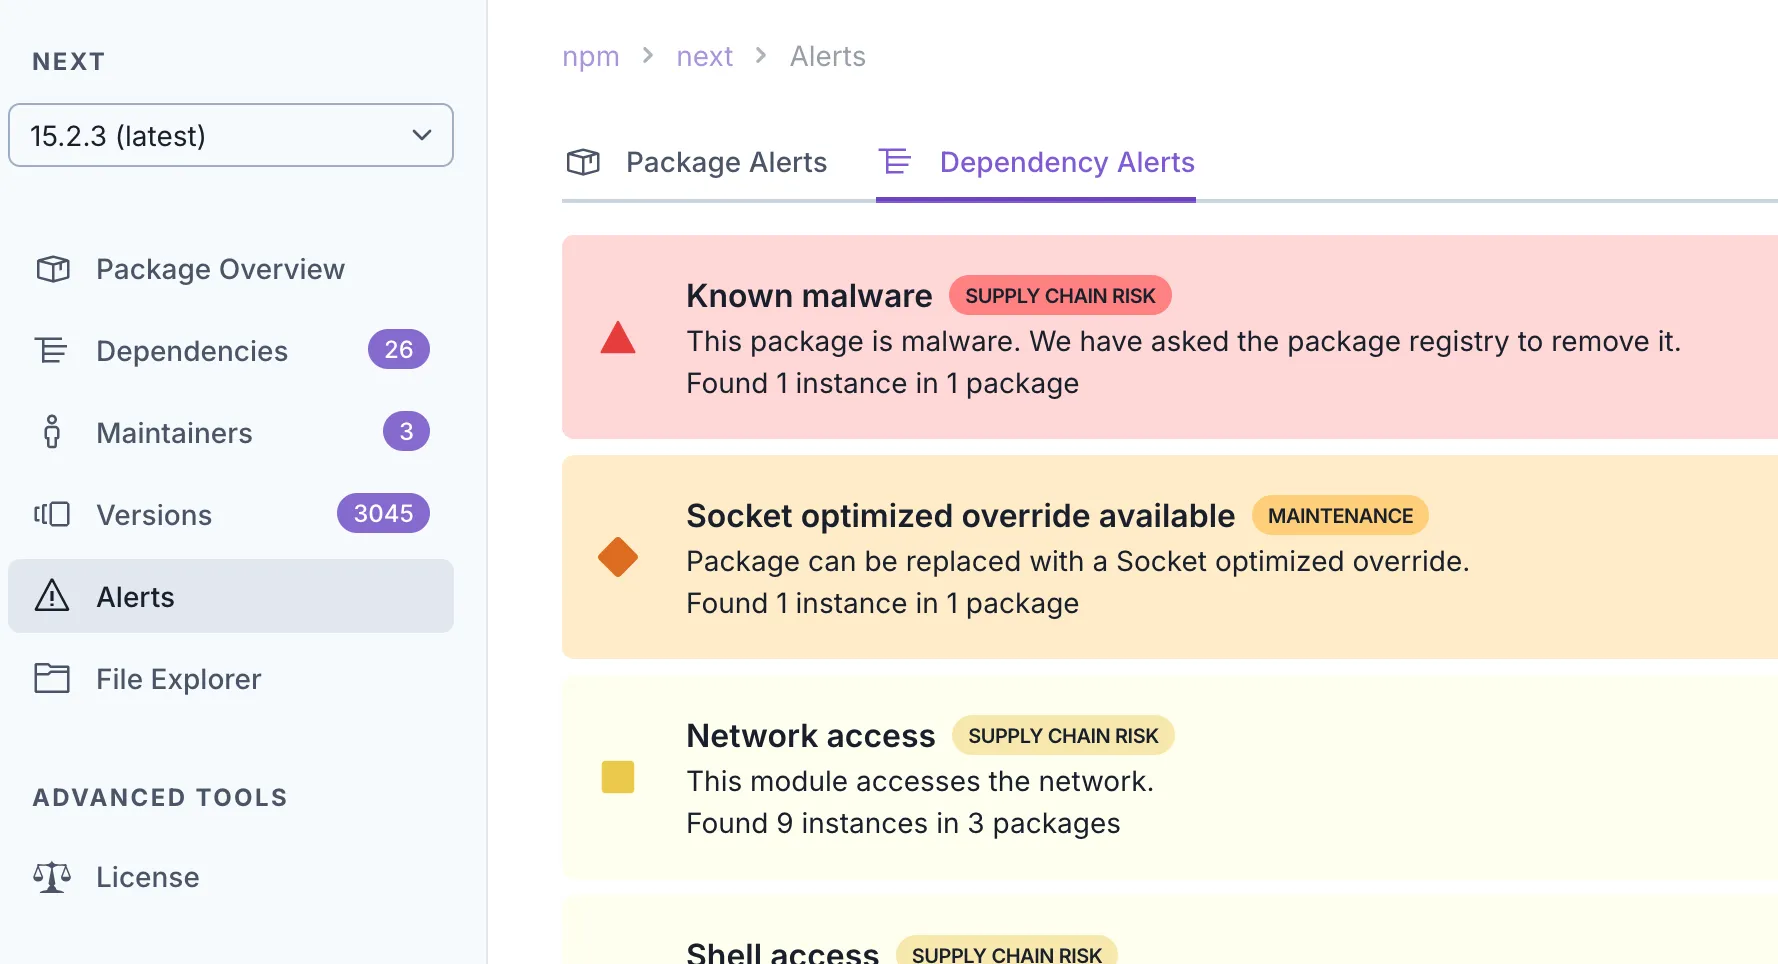
Why does socket.dev report that the latest version of next.js has a malware dependency? socket.dev/npm/package/...
“Malicious code in gen-mapping (npm) Any computer that has this package installed or running should be considered fully compromised.”
 Zach Leatherman 9 replies 9 likes1 repost1 quote Original on Bluesky


