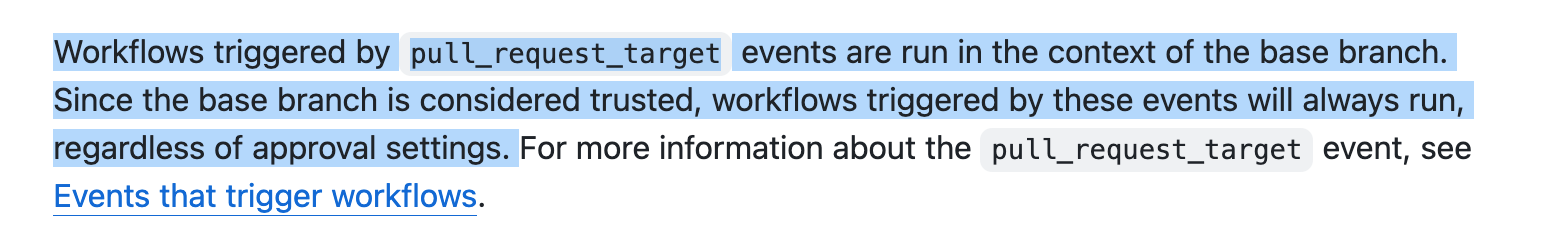
Importantly, `pull_request_target` IGNORES this GitHub security setting: https://docs.github.com/en/repositories/managing-your-repositorys-settings-and-features/enabling-features-for-your-repository/managing-github-actions-settings-for-a-repository#controlling-changes-from-forks-to-workflows-in-public-repositories

This was very surprising to me.
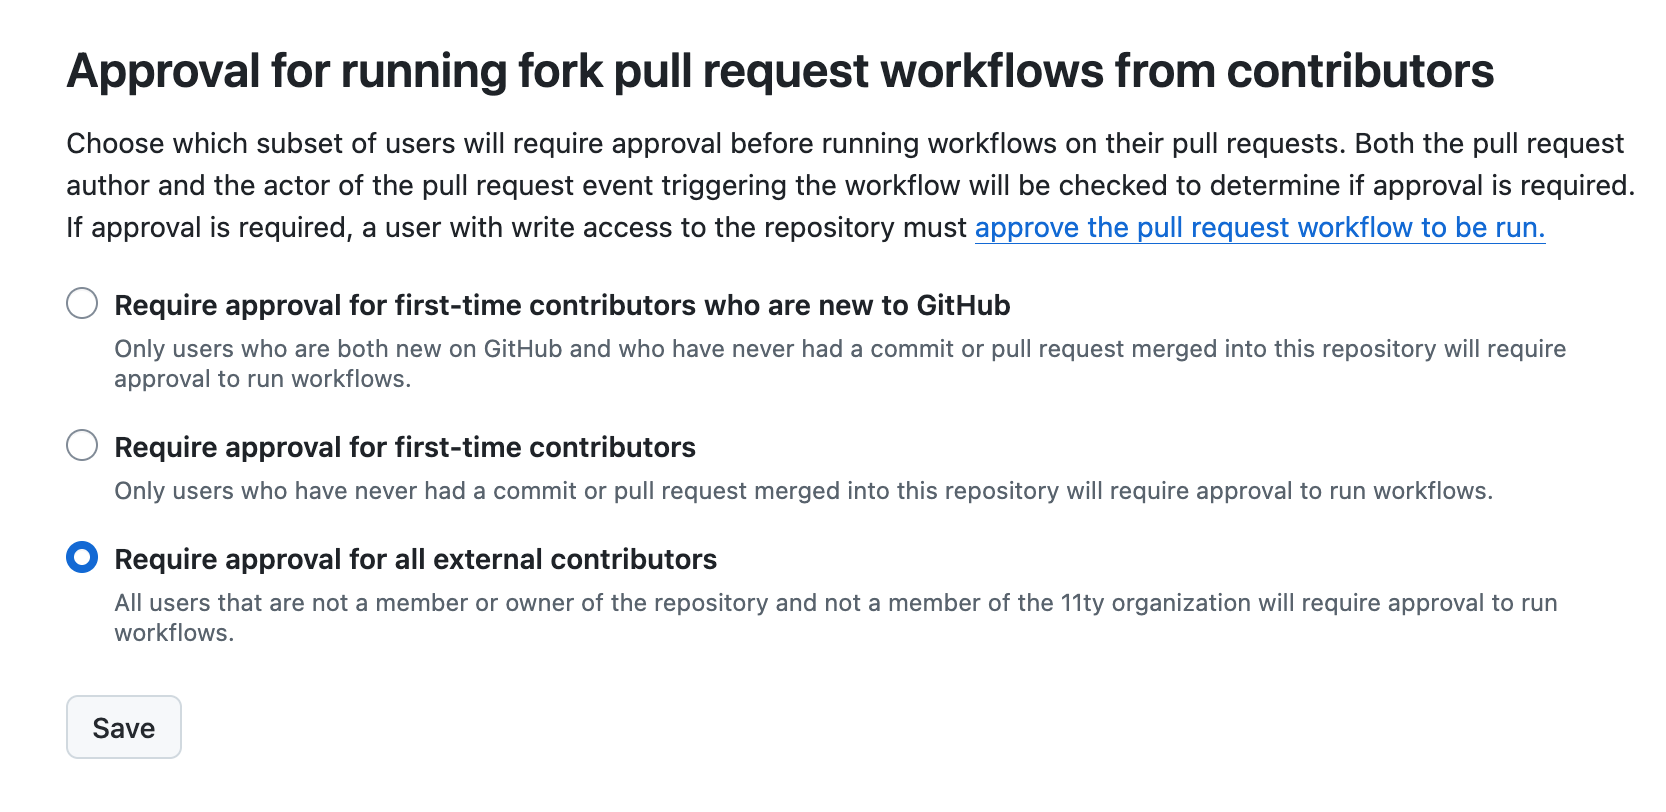
Choose which subset of users will require approval before running workflows on their pull requests. Both the pull request author and the actor of the pull request event triggering the workflow will be checked to determine if approval is required. If approval is required, a user with write access to the repository must approve the pull request workflow to be run. Require approval for first-time contributors who are new to GitHub Only users who are both new on GitHub and who have never had a commit or pull request merged into this repository will require approval to run workflows. Require approval for first-time contributors Only users who have never had a commit or pull request merged into this repository will require approval to run workflows. Require approval for all external contributors All users that are not a member or owner of the repository and not a member of the 11ty organization will require approval to run workflows. Workflows triggered by pullrequesttarget events are run in the context of the base branch. Since the base branch is considered trusted, workflows triggered by these events will always run, regardless of approval settings. For more information about the pullrequesttarget event, see Events that trigger workflows.